Key highlights:
- ZachXBT says he posed as a client to infiltrate a Chinese crime ring that allegedly laundered billions of dollars for North Korea-linked Lazarus Group.
- The undercover probe involved $349,700 in transactions and helped identify more than $12 million in funds linked to the $1.5 billion Bybit hack.
- The investigation contributed to crypto freezes, including around $442,000 in USDT, while exposing a broader network used to move illicit funds.
Onchain sleuth ZachXBT infiltrated a Chinese organized crime syndicate by posing as a client, spending hundreds of thousands of dollars to gather intelligence that helped freeze funds linked to the $1.5 billion Bybit hack. The on-chain investigator said the operation gave him direct access to a money-laundering network he linked to hackers associated with North Korea’s Lazarus Group.
ZachXBT posed as a client in undercover operation
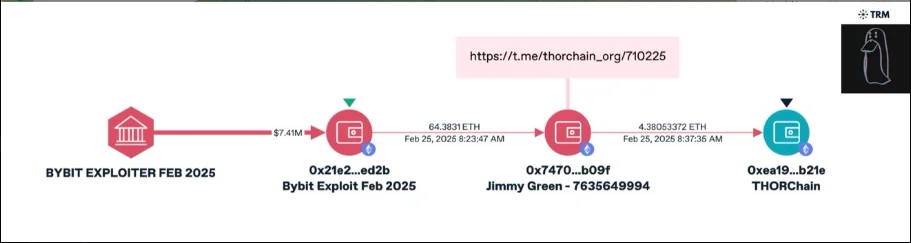
Following the February 2025 Bybit hack, ZachXBT said he found more than 15 accounts in public Telegram and Discord groups seeking help processing transactions involving stolen funds.
He eventually contacted an operator using the alias “Jimmy Green” and presented himself as a potential client. ZachXBT said he used multiple USDC and USDT transactions to build trust with the operator while accepting roughly 5% losses on individual orders in exchange for intelligence.
Per the
The funds moved across Bitcoin, Ethereum, Solana, and Tron as the network attempted to obscure their origin. ZachXBT also identified a transaction in which information provided by the operator about an upcoming bridge transfer matched activity recorded on THORChain.
The investigation eventually produced a concrete result. Tether froze roughly $442,000 in USDT connected to the wallet cluster, according to ZachXBT. He also said his investigation helped confirm a separate freeze involving 332,000 USDC connected to the Poloniex hack.
Investigation exposed wider laundering network
ZachXBT said the operation extended beyond the Bybit attack to include other ecosystem exploits.
The investigator traced approximately $3 million in fraudulent proceeds discussed by the operator to a wallet associated with Huione Guarantee, a Cambodian financial network that U.S. authorities later targeted over money-laundering concerns. FinCEN identified Huione Group as a financial institution of primary money-laundering concern in May 2025.
ZachXBT said the intelligence gathered during the undercover operation was provided to private-sector investigators and law enforcement agencies involved in the case.
The FBI previously attributed the February 2025 Bybit theft, worth about $1.5 billion, to North Korea and referred to the activity as TraderTraitor. ZachXBT now says the Chinese syndicate he infiltrated had laundered more than $1 billion across multiple exploits for actors linked to Lazarus Group.
ZachXBT said the investigation also carried a personal risk and required him to absorb substantial financial losses. Since 2022, he claims to have helped facilitate the freezing of more than $75 million linked to North Korea-related crypto incidents.
Source:: ZachXBT Went Undercover Inside Chinese Ring That Laundered Billions for Lazarus