Key highlights:
- Revolut has handed over the private details of some of its customers to bad actors via a carefully orchestrated scheme mimicking an official request from regulators
- The bad actors are leaking sensitive customer data after demanding payment from the fintech
- Revolut says customer funds remain safe, but attackers threaten to release more customer data and internal company information
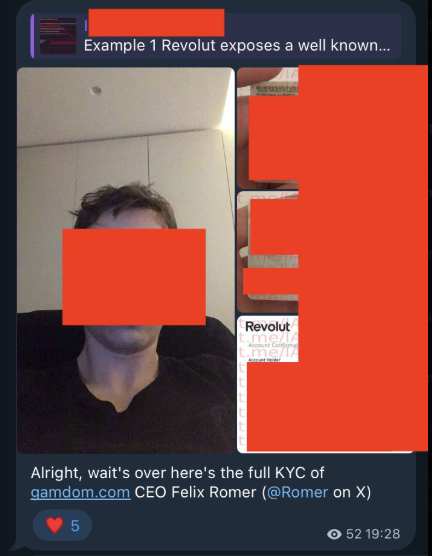
British fintech Revolut is facing an escalating extortion campaign after attackers began publishing sensitive customer information obtained through a fraudulent data request. The exposed records reportedly include Bitcoin transaction histories, with the bad actors demanding payment from Revolut to pause the leaks.
Revolut hands over customers’ data to bad actors
Revolut has via X
The attackers are now demanding payment from Revolut and threatening to release more customer data, private messages, and information about the fintech’s internal operations. However, an exact ransom fee has yet to be made public, but the framing suggests that Revolut is unwilling to accede to their demands.
The attackers also accuse Revolut of allowing sensitive customer information to reach countries outside its jurisdiction, alleging the fintech was negligent in protecting customer privacy.
While Bitcoin transactions are visible on-chain, linking those transactions to a person’s passport, address, phone number, and other identifying information can pose risks. The attackers can connect real-world identities with historical Bitcoin activity, teeing up potential crypto-wrench attacks.
Last week, Trezor disclosed that over 60,000 of its US customers were victims of a data breach involving one of its shipping partners. Trezor also suffered a third-party email provider breach, providing bad actors with the tools to send a barrage of phishing emails to users of its hardware wallet.
Source:: Revolut Hackers Leak Bitcoin User Data as Extortion Threat Escalates